Suspending a strategic activity, communicating without having all the information, balancing operational, financial, legal, or reputational imperatives… In a cyber crisis, executives must make complex and urgent decisions, the consequences of which can have a lasting impact on their organization. A cyber crisis exercise for an Executive Committee or Management Committee allows leadership to confront these situations and test their ability to make decisions collectively.
While companies have gradually strengthened their capabilities for detecting and responding to cyber incidents, preparing leadership bodies remains a major challenge. A cyber crisis is not just a technical problem. It becomes a business crisis when it threatens business continuity, undermines stakeholder trust, or requires strategic trade-offs.
The goal of a cyber crisis exercise for a COMEX or a CODIR is to confront leaders with these situations and to identify, before a real crisis occurs, the weaknesses of their organization.
Why specifically train the COMEX or CODIR in cyber crisis management?
In a cyber crisis situation, the COMEX is not intended to oversee the technical resolution of the incident. Its role is to make decisions that bind the company. A cyber crisis management exercise helps leaders work on this posture and test the collective mechanisms that support their decision-making.
📎 Interested in the topic? Discover everything you need to know about cyber and hybrid crisis management exercises
Distinguishing strategic management from technical response
In the face of a major cyberattack, technical teams conduct investigations, assess impacts, and organize remediation. Governing bodies, for their part, must assess the consequences of the incident on the entire organization, set priorities, arbitrate between sometimes conflicting interests, and take responsibility for the resulting decisions.
This responsibility is exercised in an uncomfortable environment: information is fragmented, assumptions evolve, experts do not always have definitive answers, and decisions cannot systematically wait.
One of the main challenges for a Executive Committee is precisely to accept deciding without knowing everything. A cyber crisis exercise for executives allows working on this ability to arbitrate in uncertainty, without replacing the teams responsible for operational response.
Testing the collective functioning of the crisis unit
The exercise also allows testing the mechanisms that make collective decision-making possible: the distribution of responsibilities, the coordination between operational and decision-making cells, information flow, the formalization of arbitrations, and monitoring their execution.
Bringing the right people together around a table is not enough to form an effective crisis unit. Everyone still needs to know what falls under their responsibility, when to intervene, and how to contribute to a collective decision.
Cyber crisis management at the COMEX level therefore relies as much on strategic trade-offs as on the functioning of the decision-making crisis unit.
Which strategic decisions should be tested during a COMEX/CODIR cyber crisis exercise?
An exercise intended for leaders should not be a succession of technical injections to which the COMEX would be invited to respond. Above all, they must test their ability to arbitrate, prioritize, and decide.
1. Arbitrate between business continuity and risk management
A cyberattack affects several critical systems. Technical teams recommend their immediate isolation to contain the spread. But this decision would lead to the interruption of a major activity, with significant financial and contractual consequences.
- Should we prioritize the continuity of operations, at the risk of worsening the incident, or accept an interruption whose economic consequences could be considerable?
This arbitration illustrates the cross-cutting nature of a cyber crisis. It cannot be decided solely on the basis of a technical assessment. The exercise allows verification of whether managers have the necessary information to decide, whether the business consequences are properly assessed, and whether decision-making responsibilities are clearly established.
2. Deciding to communicate in uncertainty
Information related to a cyberattack begins to circulate. Journalists approach the company, employees question, and some clients ask for explanations. Yet, investigations are still ongoing and the exact scope of the compromise remains unknown.
immediately or wait for solid evidence? What can be stated without risking contradiction a few hours later?
In a cyber crisis, silence is rarely neutral. But premature or insufficiently controlled communication can also sustainably undermine trust. A cyber crisis simulation allows leaders to face these dilemmas, test coordination with communication and legal functions, and work on their ability to speak clearly, responsibly, and adapted to the level of uncertainty.

3. Prioritize activities and allocate limited resources
When several activities are simultaneously affected, not everything can necessarily be restored at the same time.
prioritize the activity generating the most revenue? The one that serves the most sensitive customers? The one whose interruption has the most significant regulatory consequences?
These decisions may reveal a gap between the theoretical priorities defined in business continuity schemes and the reality of strategic trade-offs. The exercise allows executives to confront their own priorities and verify that these are understood, shared, and translatable into operational decisions.
📎 Discover the client case: Defense Industry: orchestrating technical response and strategic decision-making in the context of a major cyber crisis.
4. Managing interdependencies and stakeholders
A cyber crisis rarely goes beyond the organization’s boundaries alone. Subsidiaries, critical suppliers, partners, authorities, insurers, and strategic clients are all actors whose expectations, constraints, and decisions can influence the course of the crisis.
Imagine a subsidiary wants to restart its operations while the group considers the risk of spread still too high. Who decides? On what criteria? And how to manage the local consequences of a central-level arbitration?
cyber crisis governance, particularly in complex or international organizations, and clarify the relationship between different decision-making levels.
5. Make long-term binding
Some decisions made in the first hours can have consequences lasting several weeks, or even months.
expenses be incurred to speed up reconstruction? Call on additional service providers? Temporarily suspend a service? Inform certain stakeholders even before having a comprehensive view of the situation?
The goal is not to seek a universally correct answer. It is to verify that leaders know how to identify options, assess their consequences, seek relevant expertise, and collectively assume their decisions.
How to design a cyber crisis exercise adapted to a COMEX or a CODIR?
A cyber crisis exercise intended for a COMEX cannot be conceived as an operational exercise to which leaders were simply invited. The objectives, pace, information provided, and proposed situations must be adapted to the level of responsibility of the participants.
An operational unit must demonstrate its ability to qualify an incident, coordinate actions, and lead the response.
A decision crisis unit must be confronted with choices that truly fall under its authority.
Starting from the organization’s stakes
The first requirement is to start from organizational stakes rather than a generic technical scenario. The business model, critical activities, digital dependencies, group organization, media exposure, regulatory environment, and the maturity of crisis mechanisms are all parameters that should guide the design of the exercise.
Building a
artificially to keep participants under pressure. They must gradually make their understanding of the situation and the decisions they have to make more complex.
Provide real spaces for arbitrage
A good exercise should give leaders the time and elements necessary to analyze options and take a position. Multiplying requests is not enough to create useful training.
The intensity of an exercise is not measured by the number of events injected, but by the relevance of the decisions it forces to be made.
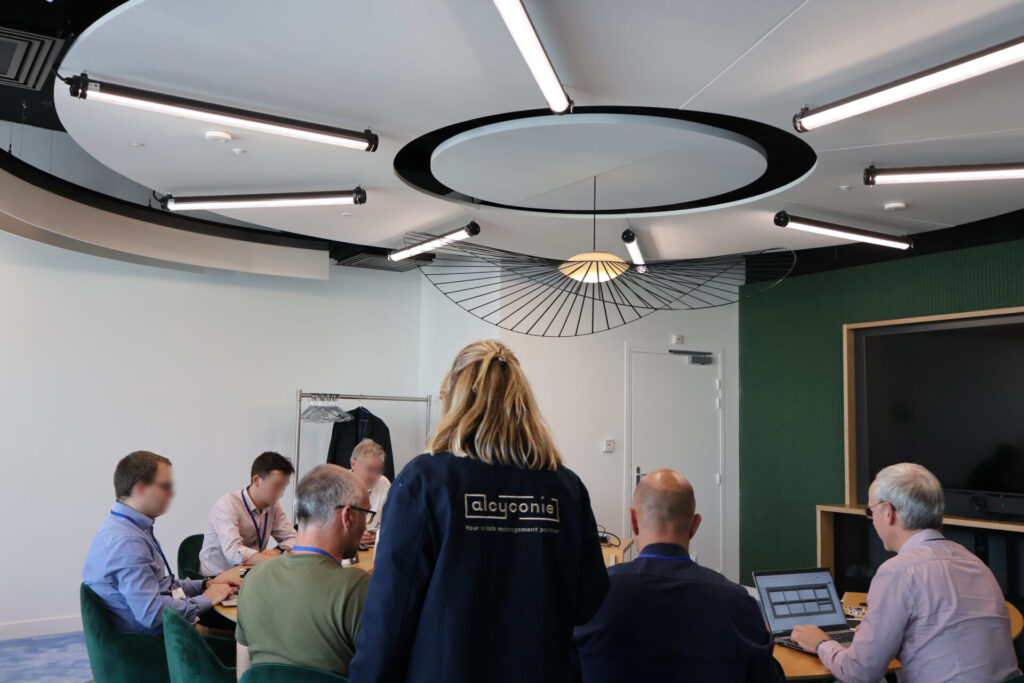
At Alcyconie, more than 100 crisis units are trained each year, about 60% of which are from COMEX and CODIR.
This experience leads to paying particular attention to the construction of decision-making dilemmas, the credibility of interactions, and the scenario’s ability to reveal the real governance mechanisms.
A successful exercise is not necessarily one in which participants reacted perfectly. It is one that brings out useful, sometimes uncomfortable, but concrete enough lessons to sustainably strengthen the organization’s preparedness.
What lessons can be drawn from a cyber crisis exercise for leaders?
the course of exercises, certain difficulties recur regularly. They do not necessarily reflect a lack of leadership competence, but often reveal weaknesses in how the organization collectively approaches and manages a crisis.
Spot the temptation to go down to the operational side
Faced with an uncertain situation, leaders may be tempted to multiply technical questions, follow investigations down to the smallest detail, or take direct control over certain actions. They then risk losing sight of their primary role: setting a course and arbitrating.
Formalizing decisions
A discussion can lead to apparent consensus without an explicit decision having been made, a responsible person having been appointed, or a deadline set. However, in a crisis, an unformalized decision risks never being implemented.
Adjusting the flow of information
Too much information drowns decision-makers in details; too little prevents them from properly assessing the situation. Finding the right level of synthesis, distinguishing facts from hypotheses, and bringing up topics requiring arbitration are collective skills that are being worked on.
Clarifying governance grey areas
The exercises regularly highlight governance issues: who can decide to discontinue an activity? How far does a subsidiary’s autonomy extend? When should the Executive Board be mobilized? What decisions should be reported to the board of directors?
These issues benefit from being addressed within cyber crisis management training rather than discovered at the heart of a real crisis.
Turning observations into concrete improvements
The value of an exercise does not stop at reporting observations. It must allow for targeted actions: clarifying delegations of power, evolving escalation circuits, improving situational support, formalizing arbitration procedures, or strengthening coordination between the different levels of crisis cells.
These lessons must then be integrated into crisis management systems and put to the test during subsequent training sessions.
Crisis preparedness is not built in an exercise. It is based on a progressive, demanding, and regular approach that allows organizations to develop their collective reflexes and decision-making maturity.
Conclusion: train leaders to make decisions during a cyber crisis, not just to react
A major cyber crisis confronts organizations with much more than just an IT incident. It questions their governance, their ability to preserve their essential activities, maintain trust, and make difficult decisions in an uncertain environment.
That is why the training of the COMEX and CODIR cannot be limited to knowledge of procedures or validation of a theoretical framework. It must allow leaders to face uncertainty, test their decision-making mechanisms, and learn to arbitrate collectively before having to do so under the pressure of a real crisis.
The challenge is not to prepare leaders for a particular scenario. It is to give them the means to face those they have not yet imagined.
Read the article
Six months after Mythos: behind the predicted "vulnapocalypse," the reality of "vuln fatigue"
28 October 2026Read the article
Foresight and resilience : why we must relearn to think the unthinkable
23 October 2026Read the article